What happens in your company stays in your company.
Qriton Flow runs AI workflows on your own infrastructure. It connects your sources, applies the right model under your policies and delivers finished work, exactly once, with a record of every run.
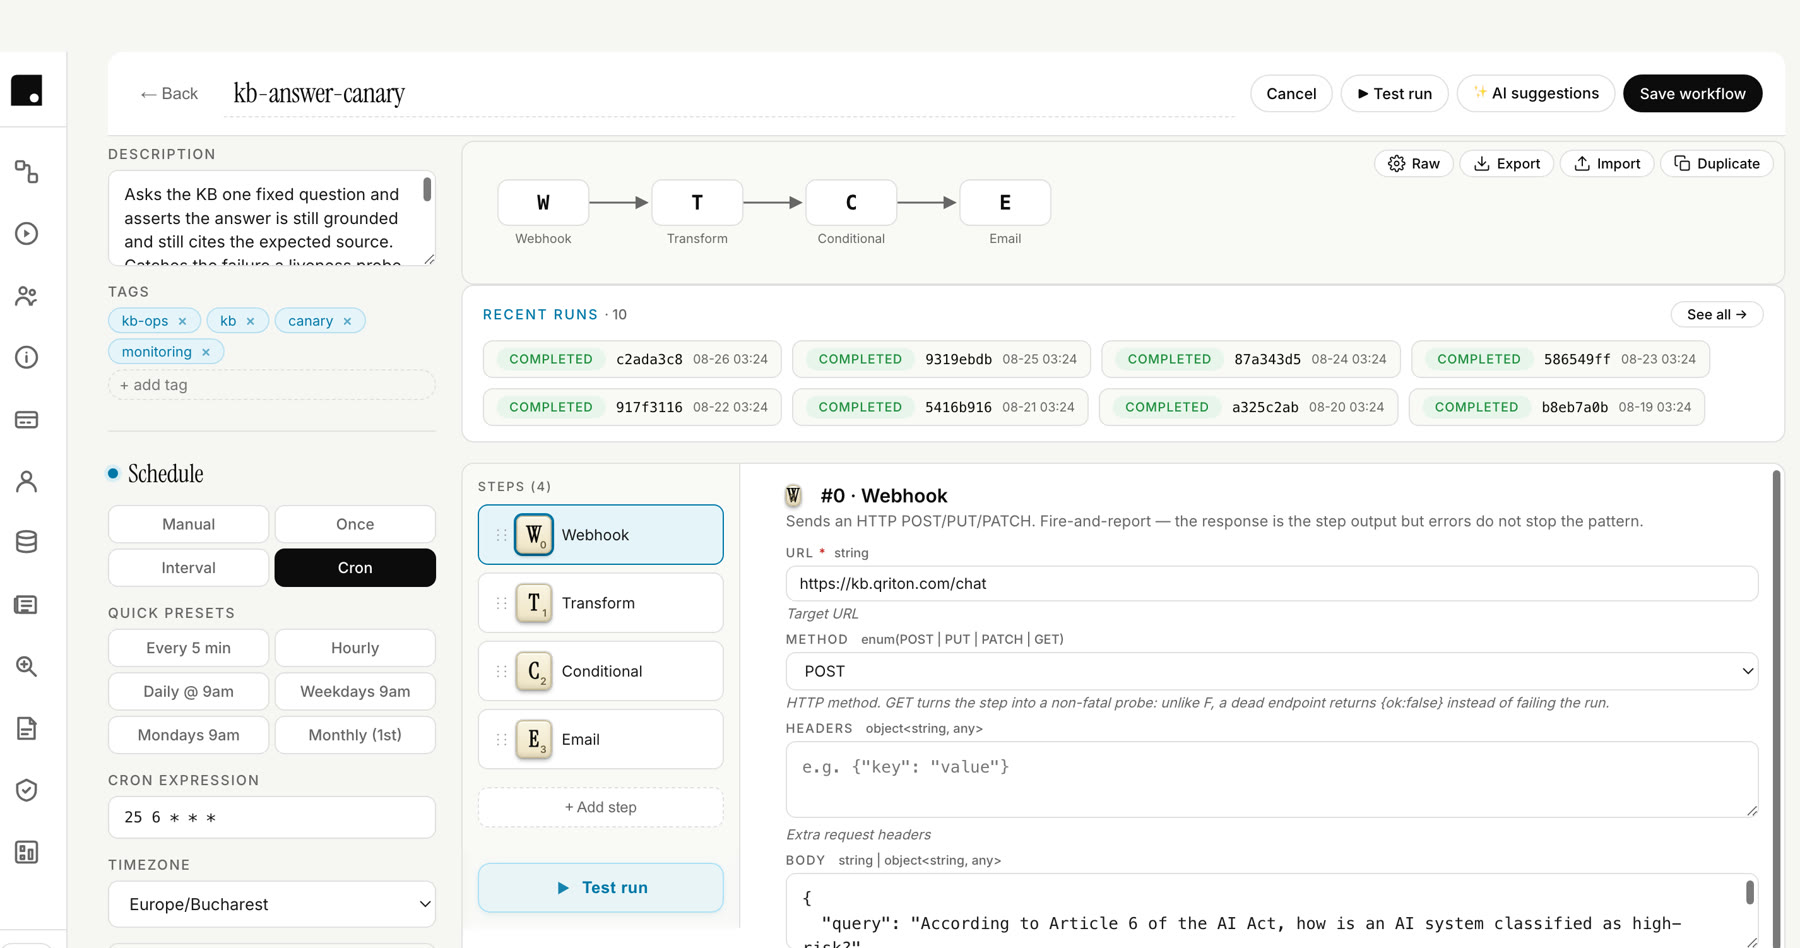
A production system for AI work, not another chat window.
When a workflow carries your reporting, your communications or your compliance obligations, “usually works” is not a standard. Flow runs every scheduled task exactly once, recovers from failure and keeps a complete record.
It is in production today, running a public media-intelligence service every day, unattended.
Every task runs once. Every run is recorded.
Exactly once
Retries, restarts and redundant servers never duplicate a message, posting or transaction.
Self-recovering
Interrupted work is detected, contained and resumed automatically.
On the record
What ran, with which model, what it produced and where it went.
From your sources to finished work.
The same platform runs a daily executive brief and a multi-stage monitoring pipeline.
Connect
APIs, data feeds, documents and PDFs, and your internal systems.
Apply policy
Models, budgets, schedules, review gates and data boundaries for each step.
Deliver
Live web reports, email, documents or downstream systems, with the run recorded.
Your model strategy, not your vendor’s.
Flow treats every model the same. Set an order of preference with automatic fallback, and change it without rebuilding a workflow.
- Open-source models
- Your selection, on your infrastructure. Air-gap ready.
- Commercial providers
- OpenAI and Anthropic, where your policy allows. Metered.
- Qriton KB
- Your organisation’s knowledge as a cited, governed source for every workflow.
What leaves your organisation is your decision.
Flow deploys inside your environment, behind a gateway you control. Outbound access is restricted by default, and with a private model a workflow runs without a single external connection.
- Identity and sign-on
- Deploys behind your identity provider or zero-trust gateway, so your sign-on and MFA policies apply first.
- Access
- Passwordless sign-in for people and individually issued keys for systems. No shared credentials.
- Encryption
- Encrypted in transit throughout. At rest, data stays in your storage under your own keys.
- Outbound access
- Validated against your policy. Every connection is recorded.
- Audit
- Every run recorded end to end, kept on your terms and exportable for review.